GitHub Actions Pipeline for Jira Ticket Agent Runs
Label triggers, scoped credentials, and Jira writeback keep agent runs useful.
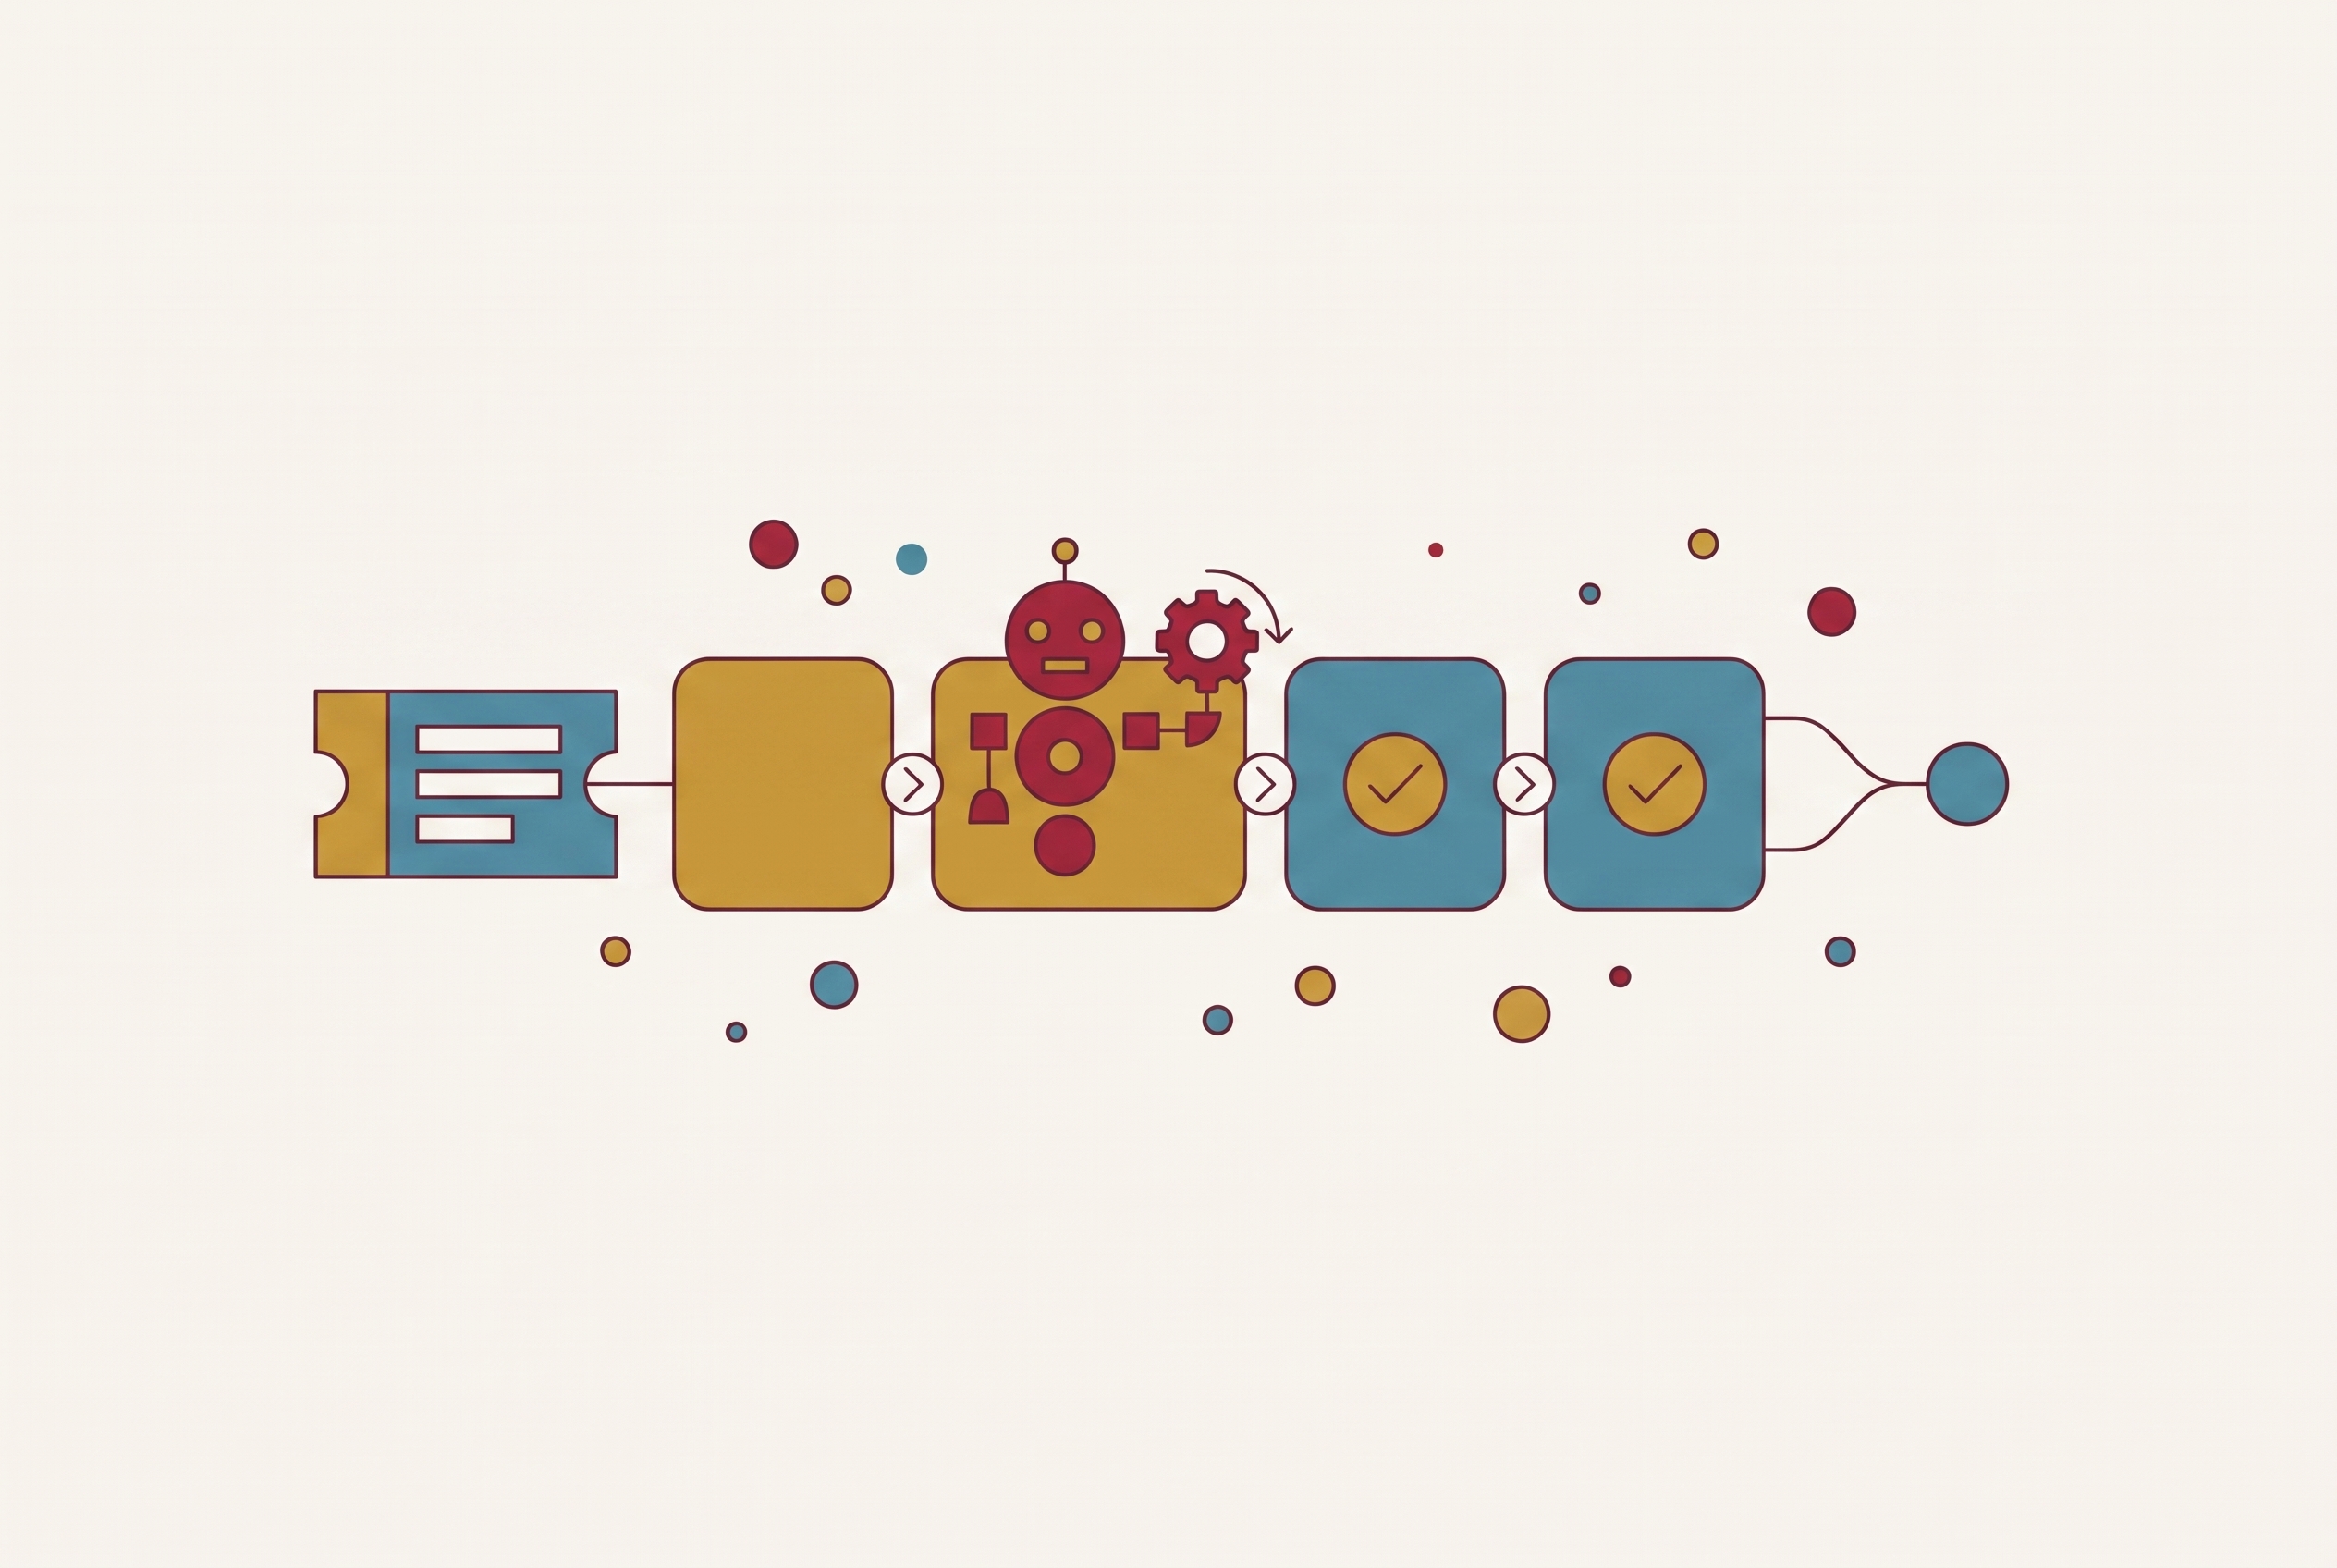
A GitHub Actions pipeline for a Jira ticket agent succeeds through its structure as well as its choice of model. An intentional trigger, validated ticket context, bounded credentials, restricted execution, and reliable status writeback form one design. Together, they keep agent runs tied to useful work rather than redundant cycles that consume runner minutes and leave Jira out of step with the repository.
Why a label-triggered workflow beats a push-triggered one for a Jira ticket agent
The agent runs, changes code, and pushes those changes, which can trigger another run on the code it just changed. Runner minutes go toward repeating work before another push supersedes the result. A label trigger changes the basis for execution. Instead of treating repository activity as a request for automation, it ties the run to a human decision to assign a ticket to the agent.
The OpenAI Codex cookbook implements this pattern with a Jira Automation rule that listens for label events and calls GitHub Actions through workflow_dispatch. The rule filters for a keyword label, such as aswe, so unrelated ticket updates do not initiate work. That second condition is essential to the trigger. Checking only whether a label changed admits unrelated label operations, while checking whether the updated labels include the target keyword restricts execution to explicitly tagged issues.
Other dispatch mechanisms suit different integration boundaries. The elisa-actions/jira-issue pattern uses repository_dispatch, allowing an external system to POST a webhook that starts the workflow. This can serve a Jira rule or support pipeline, but the external dependency needs separate protection. Scheduled polling avoids some event-infrastructure complexity but sacrifices that direct connection to intent. The scheduler wakes whether anything changed or not, reintroducing redundant activity that an event-driven design avoids.
What the pipeline receives from Jira and why ticket quality is a gate, not a detail
Once the trigger admits a ticket, the payload determines what the agent can understand about the requested change. The cookbook passes the issue key, summary, and a cleaned-up description, escaping quotes and newlines so the content parses correctly in YAML or JSON. These fields form the minimum execution context. Extra variables can pass acceptance criteria, linked epics, priority, and component to give the agent more context. However, a larger payload does not compensate for missing intent.
A summary such as “Fix login issue” leaves the expected behavior undefined. The agent has no safe basis for deciding what the requested fix should accomplish. Ticket validation therefore belongs before the first agent invocation. The label gives the agent permission to consider the work. It does not establish that the description is sufficient to perform it.
Bitmovin’s one-shot workflow illustrates why this boundary belongs in the design. Its approach is best suited to small bug fixes, localized cleanup, repetitive low-risk changes, and tasks with clearly defined expected behavior. A request that requires deep architectural reasoning differs in kind from a narrow fix, and an underspecified request needs clarification before execution.
Supporting documents can supply context that the ticket need not reproduce. The Atlassian Rovo MCP Server reached general availability in February 2026 and exposes Confluence tools including getConfluencePage and searchConfluenceUsingCql. These let an agent read architecture documents and API specifications before writing code. Those documents help explain the system around the request, but validation still has to check what change is wanted.
Storing and passing credentials without exposing them to the runner log
The validated payload describes the work, but credentials determine which systems the workflow can affect. Three credential sets have distinct purposes. A GitHub token lets the workflow write to the repository and create a PR, a Jira API token lets it read tickets and make transitions, and an agent API key lets it use the coding model. Their exposure would create different consequences, so treating them as one interchangeable collection of secrets obscures the boundaries the pipeline needs.
GitHub Actions encrypted secrets are the storage location for these credentials. The cookbook and the Jira issue action follow this pattern. GitHub provisions secrets.GITHUB_TOKEN, while JIRA_API_TOKEN, JIRA_EMAIL, JIRA_BASE_URL, and the agent key are configured manually. Shell steps should get secrets through environment variables set for each step. Direct interpolation of a secret expression into the run body writes the value into the shell command string before masking runs.
MCP authentication needs the same separation between configuration and credentials. The Rovo MCP migration guide documents Codex CLI support for native HTTP MCP transport through bearer_token_env_var, keeping the bearer token in an environment variable separate from the configuration file. This is the recommended CI path. The transport itself also needs attention because the legacy /v1/sse endpoint stops working after 30 June 2026. Its replacement is /v1/mcp, using Streamable HTTP.
Secret storage alone cannot protect a job from compromised executable dependencies. In the March 2025 compromise of tj-actions/changed-files, tracked as CVE-2025-30066, a malicious action payload exposed the runner’s secrets. Consequently, any third-party action that touches secrets or runs in the same job must be pinned to a full commit SHA, replacing any mutable tag. The broader security boundary extends beyond the step that authenticates.
The OpenAI Codex cookbook implements this pattern with a Jira Automation rule that listens for label events and calls GitHub Actions through workflow_dispatch.
Invoking the agent inside the workflow and scoping what it is allowed to do
The invocation step runs with the repository checked out, either inside a Docker image or in the runner’s working directory. It receives Jira context as environment variables or CLI arguments and runs headlessly. Its immediate output is changed files on disk. Later steps commit and push those changes, so running the model is separate from publishing what it changed.
The cookbook constructs the prompt from $ISSUE_KEY, $TITLE, and $DESC, then passes it to codex exec. The next step stages the changes with git add -A and commits them using the issue key and title. This adjacency makes the transition from generated output to version-controlled change auditable.
Bitmovin ran its one-shot workflow inside a purpose-built Docker environment containing the checked-out repository and a configured build and development toolchain. Tests ran there on their own before any PR opened. That environment supplied an execution boundary, but it did not remove the need to restrict task scope. Small, clearly specified changes fit this approach. Refactors, complex features, and tasks requiring deep architectural reasoning do not fit the same one-shot assumption.
A quick-fix label can select a narrow bug-fix prompt, while a refactor label can be excluded or directed to a human-review gate. GitHub Agentic Workflows provides a complementary permission model through read-only defaults and preapproved “safe outputs” for write operations. Custom pipelines should replicate that default-restrictive posture regardless of tooling. The resulting guardrail limits what the agent may publish before a person reviews the change.
Writing ticket status back to Jira after the agent finishes
The status loop starts before the agent runs and ends with an update after the PR opens. Transitioning the ticket to “In Progress” signals that the work has been claimed. Once the PR opens, the workflow transitions the ticket to “In Review” and posts the PR URL as a comment. Otherwise, the board remains misleading. A ticket left in “To Do” can invite someone else to duplicate work that already has a proposed implementation.
The cookbook demonstrates Jira REST API writeback through transition and comment requests. A status change uses a POST to /rest/api/3/issue/{key}/transitions with the target transition ID, while the PR link goes to the issue’s comments endpoint. The workflow-specific transition ID can be retrieved at workflow authoring time through a GET to the transitions endpoint and configured for the target workflow, or fetched dynamically during execution.
Reusable actions can replace direct REST calls where teams prefer prebuilt steps. appleboy/jira-action wraps transitions, while the Jira issue action supports issue creation and resolution, with authentication and field mapping passed through inputs. These wrappers reduce the need to maintain raw curl calls. They do not remove the need to handle unsuccessful updates explicitly, because an authentication or transition failure still leaves the ticket inconsistent with the repository.
A failed transition POST must therefore fail its step so that the run cannot hide it by reporting success. Logging the HTTP response code makes failures such as an incorrect transition ID, a permission error, or a network timeout visible. Opening a PR is not the only completion condition. Reliable automation also depends on Jira accurately showing where that work now stands.
Preventing supply-chain compromise in a pipeline that holds Jira and GitHub credentials simultaneously
A job holding a Jira API token, a write-capable GitHub token, and an agent API key concentrates access across the ticket system, repository, and coding model. Compromising one action in that job can expose all three. The job boundary determines which credentials a compromised dependency can reach, so credential placement belongs in the pipeline design.
The changed-files payload read secrets from runner memory and printed them after encoding them twice with base64, bypassing GitHub’s log masking. Workflows pinned to a full commit SHA were unaffected because they did not follow the compromised mutable references. Masking was not a defense against that execution path. Every third-party action in a secret-bearing job needs SHA pinning, including PR-creation actions such as peter-evans/create-pull-request, replacing tags such as @v6.
Permissions and isolation limit the consequences if execution is compromised. The GitHub token should request only the access the job needs, including write access to pull requests and repository contents, with repository-admin scope excluded. Where the structure permits, the agent-invocation job should be separate from the Jira writeback job. The former needs the agent key, while the latter needs the Jira token. Secrets should share a job only when its step logic requires them together.
Augment Cosmos connects Jira to shared agent sessions through MCP with persistent ticket context, keeping credential management within that controlled layer and separate from workflow files. Port’s coding-agent pattern similarly separates orchestration from direct credential exposure in individual steps.
Where native Jira automation reaches its limits and why externalizing the agent logic to GitHub Actions is the right architectural call
Native Jira automation serves explicit fields and transition rules rather than interpreting free-form descriptions of intended software behavior as a coding agent does. Its execution limits also constrain orchestration. Those limits apply primarily to global and multi-project rule executions, while single-project rules are unlimited. Rules that breach the limits are marked THROTTLED in the audit log and may be disabled.
Moving agent orchestration to GitHub Actions places that execution outside Jira’s quota boundary. It also makes the workflow logic version-controlled and auditable beside the repository it modifies. Jira still holds the ticket that states the request and tracks progress, while the code-changing work runs in the repository. This division follows the work itself. The agent needs the codebase, and its proposed changes need the repository’s review controls.
Teams should still assess Atlassian-native execution, especially if they already have work built on Forge. Atlassian is migrating custom automation integrations to Forge, where async compute billing begins July 1, 2026. The Forge LLMs API is generally available and can call Claude models without external keys or data leaving Atlassian, and the Forge MCP Server is also generally available and lets coding agents write Forge code. These capabilities change the integration options. They also make runtime cost and placement explicit architectural considerations.
Rovo MCP and the “Agents in Jira” open beta, launched in March 2026, extend those options further, including agents appearing as assignees on Jira boards. Neither removes the execution-quota constraint or supplies GitHub Actions’ version-controlled, code-adjacent workflow structure. For teams whose primary artifact is code in GitHub, that structure supports the stronger architectural choice. Trigger design, credential boundaries, restricted invocation, and Jira writeback belong together because they govern one passage from an authorized ticket to a reviewed code change.
Sources
- Automate Jira ↔ GitHub with Codex
Supplied the label-triggered workflow_dispatch pattern, payload fields, codex exec invocation, and Jira REST writeback steps.
- GitHub - elisa-actions/jira-issue: Github Action for creating JIRA issues · GitHub
Provided the repository_dispatch pattern and the example of issue creation and resolution through action inputs.
- GitHub - appleboy/jira-action: CI/CD integrate with Jira Data Center on premise · GitHub
Illustrated a reusable action that wraps Jira transitions as an alternative to raw REST calls.
- GitHub Agentic Workflows
Described the read-only defaults and preapproved safe outputs model for agent write operations.